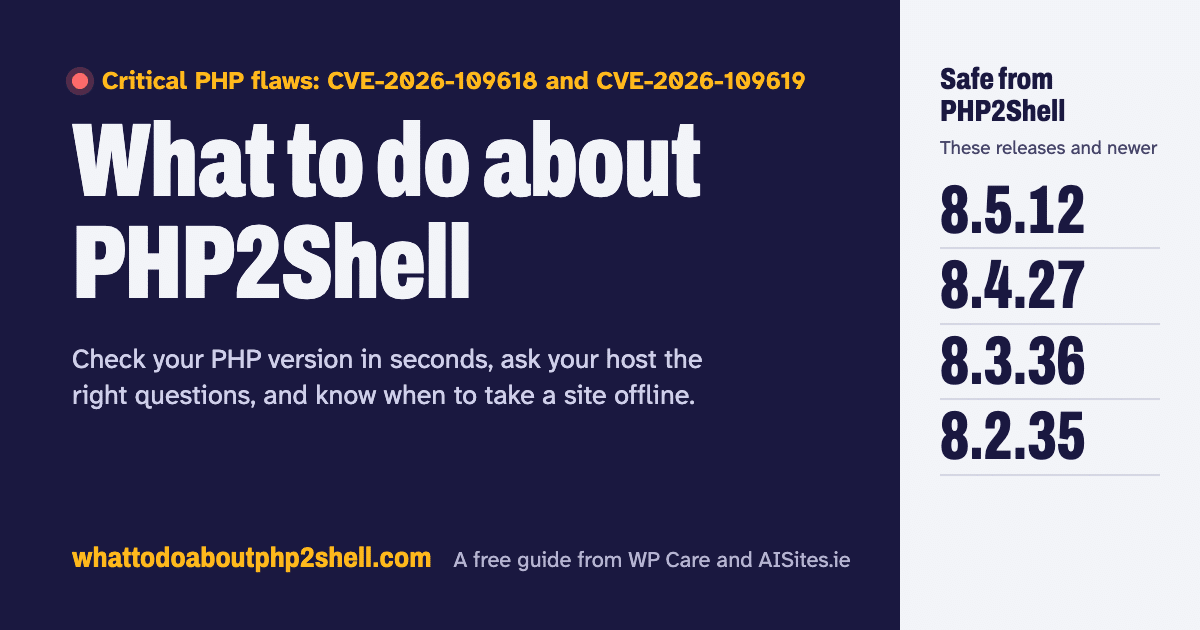
We’ve published a free guide to PHP2Shell at whattodoaboutphp2shell.com. It is for anyone with a website running on PHP, not only WordPress sites, and not only our clients.
PHP2Shell is the name given to two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, fixed on 21 October 2026. We covered the release in yesterday’s post. The fix is a PHP update on the server, so updating WordPress, a theme or a plugin does not fix it. On most hosting, the host has to apply it.
What’s on the site
- A version checker. Enter your PHP version and it tells you whether it’s fixed. The check runs in your browser.
- The fixed versions: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, plus what to do on 8.1 and older, which have no official release.
- Guides by situation: shared or managed hosting, WordPress, self-managed servers, agencies, taking a site offline, and checking whether a site was compromised.
- Ready-to-send emails to your host, or to your clients if you look after sites for others.
- A host status page, and links to the advisories from the PHP project, CISA, the UK and Irish NCSCs, ENISA and the security firms tracking attacks.
Who it’s for
The guide is written for site owners who don’t manage their own server: what to check, who to ask, and what to do if the host hasn’t patched yet.
For sites we host, PHP was updated on all WP Care servers on 21 October. No action is required from our clients.
