PHP Critical Security Release, 21 October 2026: What It Means for WordPress Sites
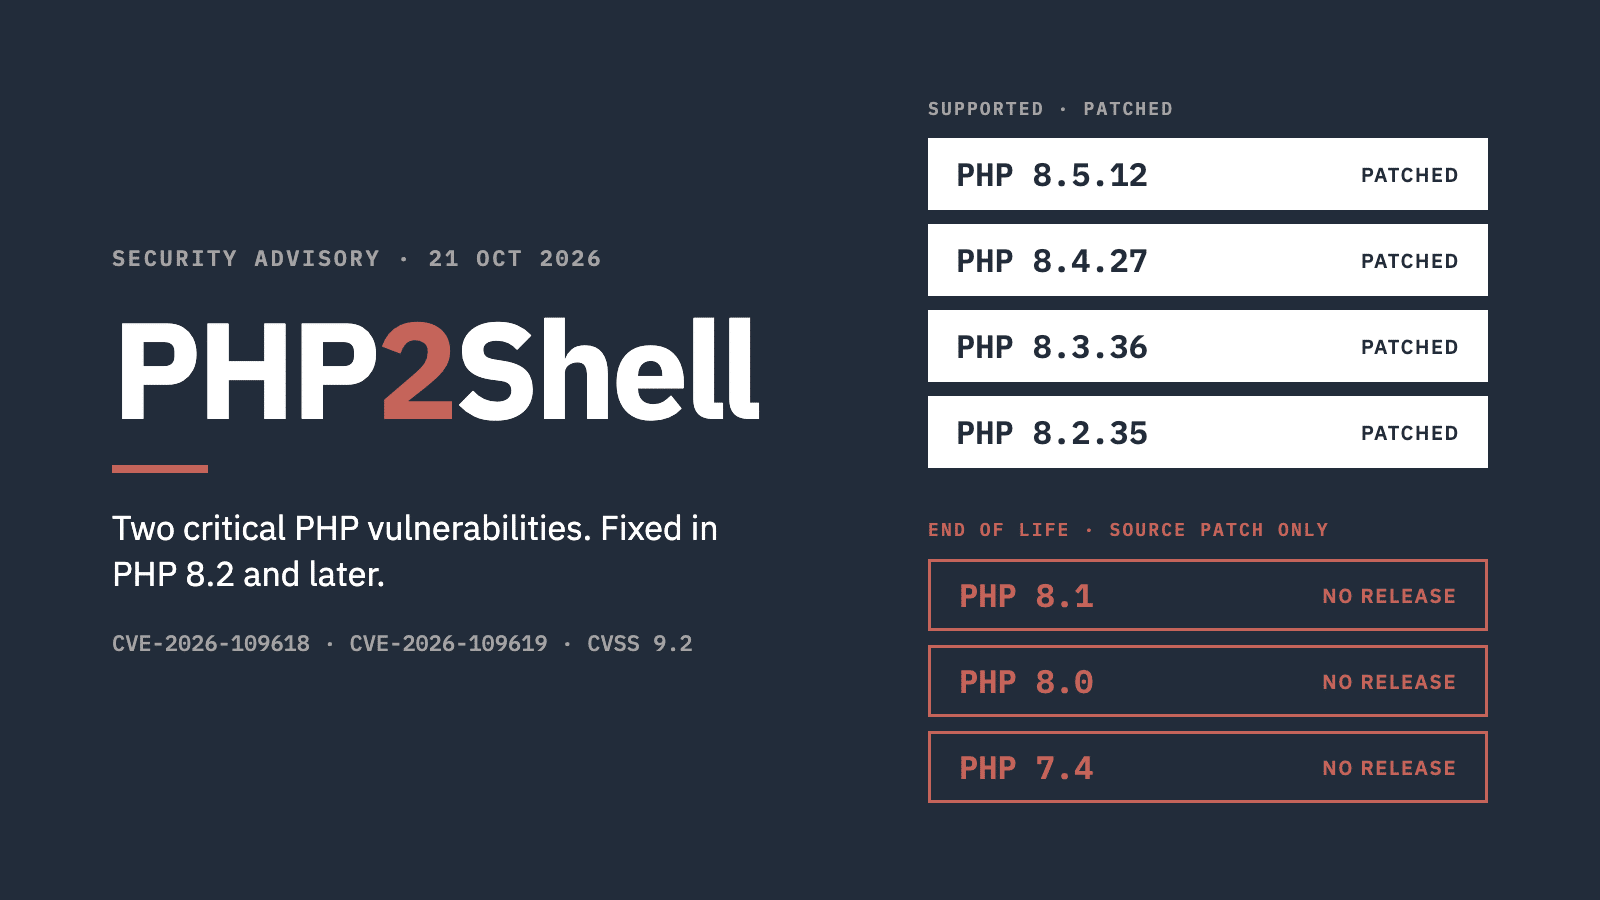
PHP released fixes for two critical flaws on 21 October 2026. What it means for WordPress sites, and why sites on old PHP versions are most at risk.
Read More
PHP released fixes for two critical flaws on 21 October 2026. What it means for WordPress sites, and why sites on old PHP versions are most at risk.
Read More
Stolen UpdraftCentral keys were used on 18–19 October 2026 to install backdoor plugins on WordPress sites. Who is exposed and what to do.
Read MoreWordPress 7.1.3, released 6 October 2026, fixes seven security issues in core, including two cross-site scripting flaws and a SQL injection in export.
Read More
WordPress 7.1.2, released 22 September 2026, fixes a critical unauthenticated file inclusion flaw. It is the fifth core security release since 17 July.
Read More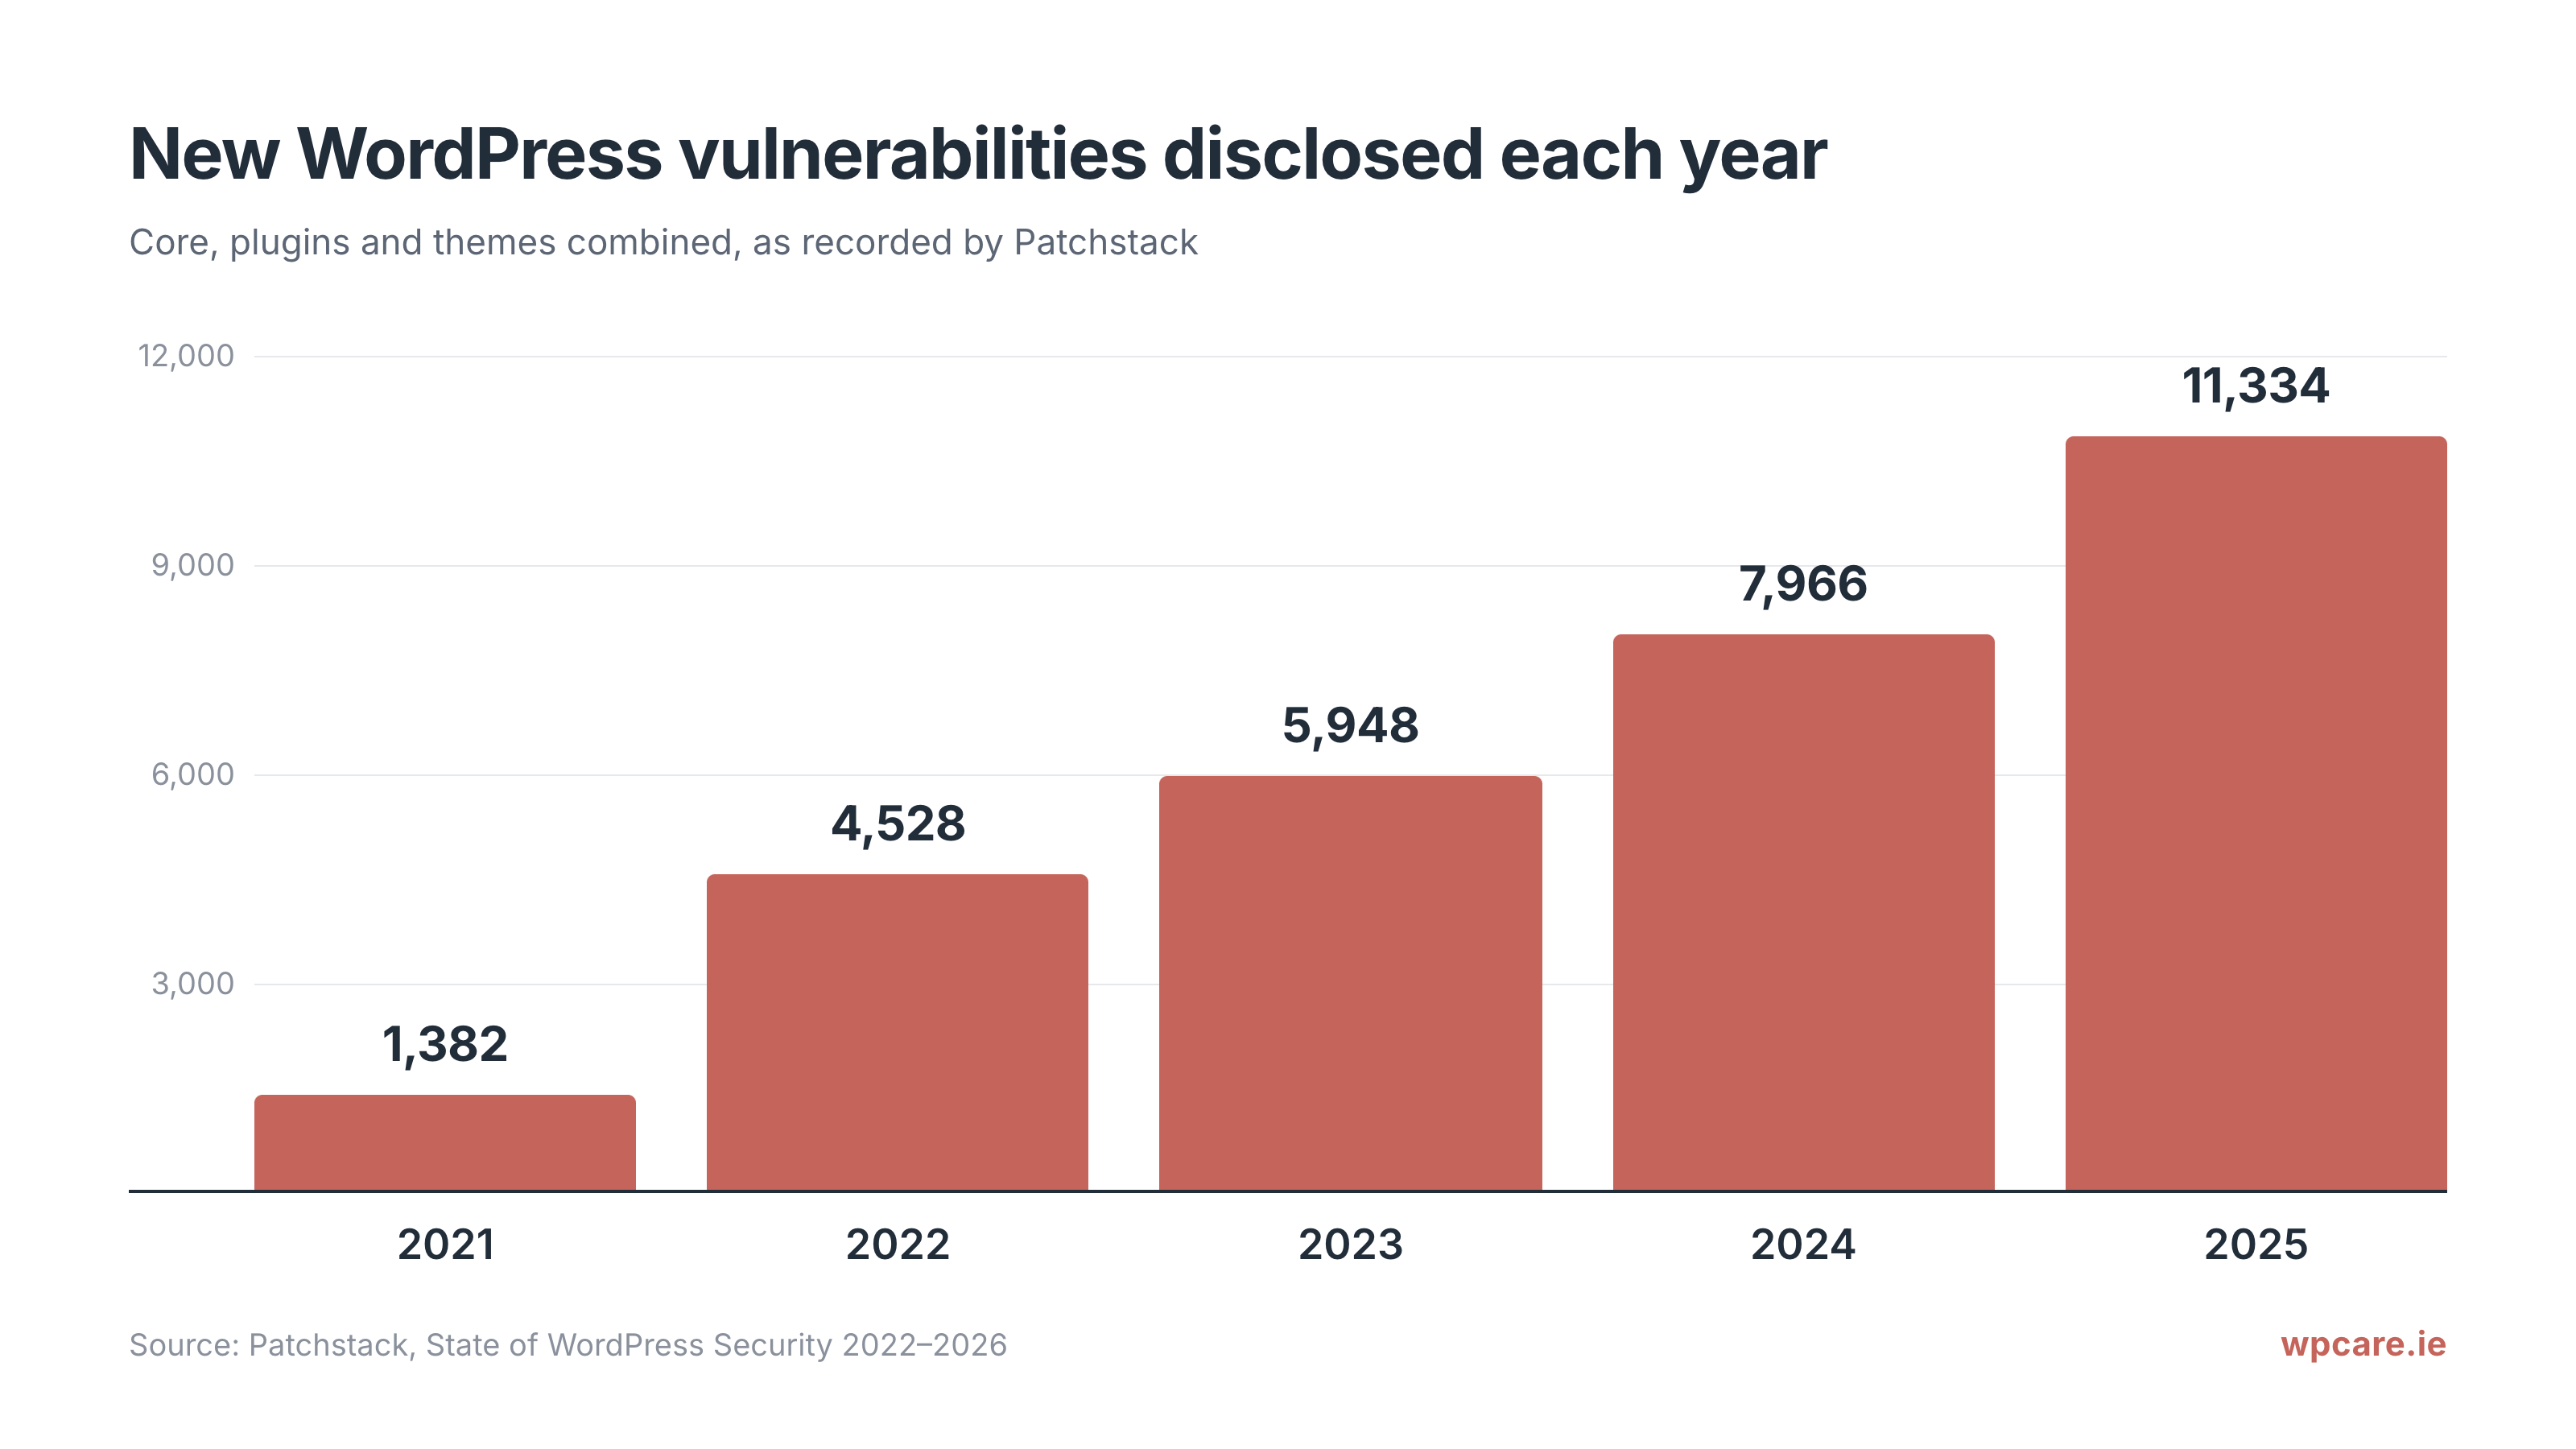
Patchstack recorded 11,334 new WordPress vulnerabilities in 2025, up 42%. Our own analysis of the CVE record shows 2026 running level, not higher.
Read More
Elementor Pro 4.2.2, released 19 August 2026, fixes a CVSS 9.0 flaw letting anyone upload PHP files through a Form upload field. What it means for your site.
Read More
WordPress 7.0.4, released 12 August 2026, fixes a remote code execution flaw — the third core security release in four weeks. What it means for your site.
Read MoreWordPress 7.0.2 was released on 17 July 2026, fixing an unauthenticated RCE and a SQL injection in core. What it affects and what to do.
Read More
Updated 15 May 2026 · Written by Andrew The short version: if your site is hosted with WP Care, you don’t need to do anything — we’ve already protected...
Read More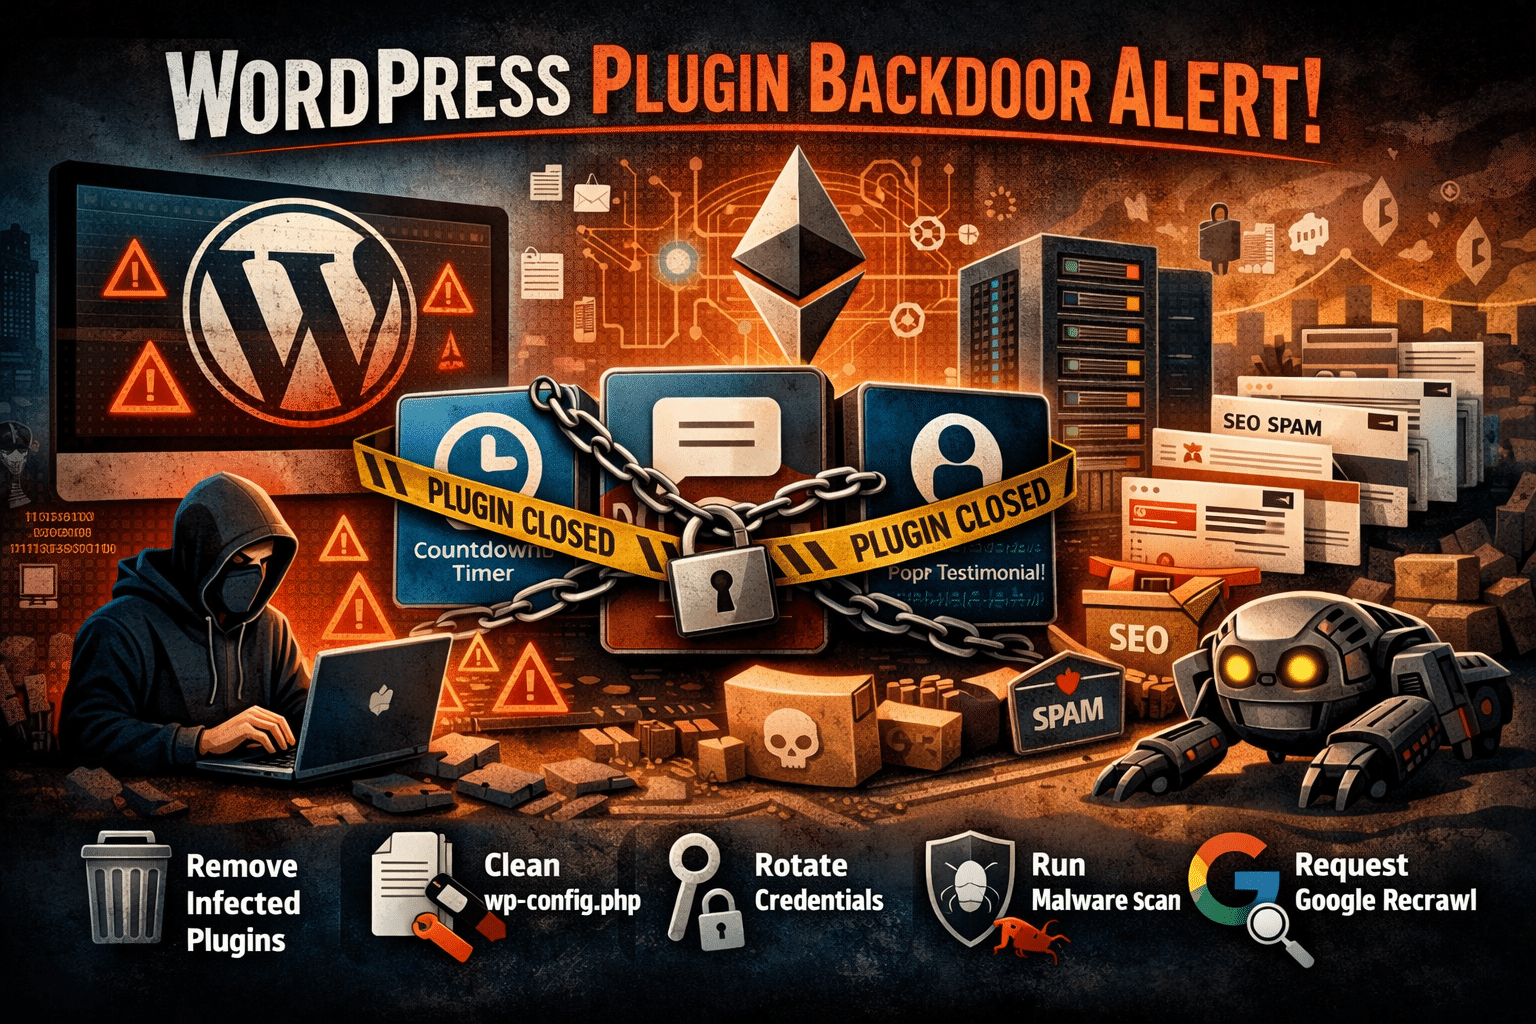
If you run a WordPress site, you’ll want to read this one carefully. Over the past fortnight the WordPress security community has uncovered one of the most significant supply...
Read More